Document created
An initial version of this presentation brings together the software pages and the contract example.
This is the starting point of the history shown here.
Resources
Explanations of the software, its uses and how it works.
In this example, the first version of the contract is kept.
68 articles
A technical guide for IT teams on S3 storage, versions, events, replication and record verification.
A document evolves, an authorization expires, a decision is revised. Months later, a team needs to recover the information it relied on. KARL's Memory Layer keeps versions, links and operation traces. But this memory must also survive incidents.
From a support case to a signed pack and on-site acceptance tests: how a customer can verify an S3Guardian fix.
How the KARL Core memory layer links versions, approvals and decisions to help teams understand a regression and recover the context of a change.
How an investigation team turned a USB drive into a verifiable case file, and why its lawyer could prove it alone, offline, eighteen months later.
An Australian reporter attends KARL's Ljubljana presentation and files an unsparing account: database-free architecture, a 3-second restore, and pricing still to be written.
A customer disputes a loan refusal eight months after the decision. Answering that requires proof the ombudsman can verify themselves, without having to trust the organization that produced it.
Eight months after a supplier's access was extended, an internal audit asks a simple question. Answering it means recovering not today's state, but the one that existed at the moment of the decision.
A company believes it has secured its future with regular backups. The day it truly needs to switch providers, it discovers backup isn't enough: it's the memory of its data that needs to be able to travel.
A fictional scenario shows how a DPO handles requests for access, an explanation of an automated decision, and erasure in KARL MX.
A credit scenario illustrated in KARL MX shows how versioned states, the temporal graph and governed retrieval reconstruct ARIA's decision in a sealed Evidence Pack.
An insurance scenario illustrated in KARL MX shows how state versioning, the temporal graph and governed retrieval identify the documents and versions NOA consulted.
Object storage provides capacity, configurable retention and API access. Business continuity also requires preserving data identity, context and governed history.
Within a supported workflow, KARL Core links data, transformations and decisions to resources from file creation and preserves their history beyond the boundaries of a Git repository.
After a ransomware attack, bringing systems back online is not enough; the restored data still needs to be assessed for trustworthiness.
A delivery package can contain several representations of the same state and their associated components. KARL Core describes them and distinguishes storage copies from a new business version.
KARL Core distinguishes a resource, its location and its reference sources to preserve a drawing’s history through moves and renames.
Knowledge Layer links data across sources; Memory Layer preserves their state and context over time. The article explains how the layers differ, work together and where memory begins.
A decision made by an agent is not just its answer. You need to be able to retrieve the data, the rule, the authorization and the context that made it possible. That is the angle StorageNewsletter chose to present StratoFoundry.
In 1997, an engineering thesis at EPITA described distributed objects with their own usage and transformation rules, classified into three categories: white box, grey box and black box. Twenty-nine years later, the idea lives on in PanglotOS and its more than 150 polyglot services, and in the KARL core project.
The NIS2 directive no longer merely requires the implementation of security measures; it mandates proof that every action has been carried out. A chain of custody based on timestamping, versioning and WORM storage becomes indispensable for essential and important entities.
The NIS2 directive requires every security action to be transformed into reliable, timestamped, and immutable evidence. Combining WORM storage, S3 Object Lock buckets, and a cryptographic chain of custody creates a comprehensive pipeline of legally admissible evidence, essential during audits or forensic investigations.
Organisations accumulate petabytes of so-called "dark data" every day: files, logs, emails and obsolete databases outside governance processes. This article examines their costs and risks, potential AI uses and the controls needed before use.
Legacy monoliths write their audit logs to local disk, which often results in insufficient legal traceability. Migrating these streams to S3 storage with Object Lock, versioning, and the Rust SDK enables legal immutability while reducing operational costs.
Organisations must not only secure data in the cloud, but prove that every file operation complies with regulations. This article explains how to build an immutable Rust audit library producing a chain of evidence suitable for auditing.
Insurers want evidence that critical data is protected and recoverable. This article outlines their requirements and data-protection architectures, then examines how AI can automate monitoring, optimise backup strategies and generate audit evidence. It ends with an implementation scenario for an industrial SME.
LTO and strip remove unnecessary symbols from Rust binaries and reduce their attack surface. A deterministic build produces the same binary from the same source code. This article explains how to configure release profiles and collect evidence for a NIS2 audit.
In critical environments, detecting and broadcasting an alert within microseconds supports resilience. This article describes a Tokio-based pipeline that pairs each event with an immutable chain of custody (qualified timestamp, SHA-256 hash and WORM storage) to provide auditable evidence for NIS2.
Industrial IoT sensors, PLCs and embedded systems generate petabytes of measurements each day. This article explains how to make these streams reliable, traceable and admissible in audits or legal proceedings. It outlines governance, quality and security practices and a reference architecture, illustrated by an industrial predictive-maintenance scenario.
Rust cdylib extensions combine high performance with C-compatible portability. Paired with zeroize, SHA-256 and UUID v4, they can be used to build plugins that meet NIS2 technical and legal traceability requirements.
Organisations can no longer rely solely on restoring systems from scratch after a ransomware attack. NIS2 requires evidence of every decision, action and control. This article examines how to limit damage and document compliance without reinstalling the entire infrastructure.
The GDPR sets data-retention requirements, but trained models may retain traces of the data used to train them. This article examines the legal requirements, technical and operational risks, machine-unlearning methods, and practices for balancing compliance, performance and cost.
NIS2 requires reliable evidence of cybersecurity measures. This article describes a Rust-based SSA (Secure Behavioural Alerts) plugin and explains how timestamping, versioning and traceability preserve each alert as evidence for an audit or investigation.
NIS2 requires irrefutable evidence of cybersecurity measures. Alerting systems must also protect the data they process. This article describes a Rust plugin using zeroize, SHA-256 and UUID v4 to create confidential payloads without exposing the encryption key.
Embedded AI processes data near sensors, while central systems still need access to it. Architectures, protocols and consistency models shape edge-to-cloud synchronisation, along with the technical, regulatory and financial risks.
Deleting a source file may leave copies in vector indexes, caches, and backups. Erasure processes must account for GDPR and CCPA requirements, residual risks, and operating costs.
A complete chain of custody tracks, secures, and preserves data throughout its lifecycle. It supports model reliability, regulatory compliance, and operational resilience, and integrates with DevSecOps and MLOps practices.
European organisations use sovereign and public cloud environments to meet data-residency requirements and benefit from economies of scale. A hybrid Data Fabric can orchestrate replication while balancing sovereignty, performance, resilience, and compliance (GDPR, NIS2).
LLMs can return obsolete procedures or contradict the current official version. Content lifecycle management, RAG, and AI governance help keep responses up to date.
An outage or compromise can disrupt or alter an AI platform, affecting trust and leading to significant operational costs and legal risks. A reliable recovery must preserve model integrity, training-pipeline consistency, service continuity, and regulatory compliance.
Mid-caps and SMEs face compliance requirements with smaller budgets and teams than large enterprises. The article explains how to build an auditable, traceable, and immutable documentary chain without spending hundreds of thousands of euros.
The EU AI Act progressively requires organisations to trace, document, and audit their use of AI. Prompts, models, and outputs become evidence that must be archived immutably and remain retrievable.
With LLMs and hosted inference services, an organisation’s ability to store, retrieve, and use its informational assets depends on a proprietary AI engine. This dependence raises technical, economic, legal, and strategic concerns.
No security policy can prevent all data corruption. Immutability keeps corruption from becoming permanent. It is the most underestimated property of modern storage architectures, and probably the most strategic.
Challenges covered KARL and the role of time in data, an issue tied to resilience, compliance, and documentary memory for businesses.
Regulators, clients, and administrators make digital sovereignty a concrete requirement. Regaining control of data calls for clear architectural choices.
Most digital vault systems rely on an intermediate database that duplicates information. This architecture increases risk and cost and limits scalability. A native S3 approach removes that extra layer.
Modern audits rarely fail for lack of work. More often, evidence is hard to find: documents are scattered, versions conflict, history is missing, and accountability is unclear.
No organisation is totally protected. The question is no longer 'will we be attacked?' but 'how long will it take us to return to a healthy state?'. Resilience is becoming the key cybersecurity metric.
AI is changing how organisations make decisions and creating new types of incidents involving models. Investigating them requires traces beyond those collected in conventional cybersecurity cases. This article covers the regulatory framework, evidence to preserve, acquisition and analysis methods, and technical and legal limits.
For twenty years, companies have relied on backups to protect their data. Backups address accidental loss, but not cyberattacks, ransomware, silent corruption, or current audit requirements.
Quantum computers capable of running Shor’s algorithm could threaten RSA and elliptic-curve cryptography. Organisations need to prepare their key-management systems (KMS) and PKIs for post-quantum cryptography ahead of 2026.
Logging AI interactions supports traceability and drift detection, but can create a database of personal information. Pseudonymisation, encryption and differentially private aggregation can help limit that risk while preserving useful observability.
Distributed tracing can incorporate Zero-Trust controls through contextual, automated and verifiable access policies. OpenTelemetry, service meshes and engines such as OPA support this approach. A multi-cloud payment platform illustrates its measurable benefits and operational constraints.
Combining GitOps and MLOps automates AI model builds, tests and production releases while supporting traceability, regulatory compliance (RGPD, IA Act) and immediate rollback.
Images from cameras, drones and IoT sensors may be used as evidence in civil or criminal proceedings. Their probative value depends on traceable provenance, integrity during storage and compliance with legal requirements.
Under NIS2, proving what an organisation did depends on how data is preserved as well as what is retained. Versioning, temporal controls and immutability are central to a compliant storage strategy.
NIS2 compliance requires proof of which data informed each automated decision, when it was used and whether it remained intact. Without sovereignty over training datasets, that proof becomes impossible.
Quantization, pruning and TinyML let IoT devices with a few dozen kilobytes of RAM run AI models. Governance must address their compliance, security and performance throughout the model lifecycle.
During a merger or acquisition, AI may be used to analyse, classify or migrate information assets. Mixing knowledge bases, models or metadata can put confidentiality, compliance and the strategic value of both companies at risk.
An audit trail can link identities and operations to the resources they consume. This helps explain storage costs, identify the activities that drive them, and define clear allocation rules.
AI agents with elevated rights need clear machine-identity governance. This article examines accountability when an agent causes an incident, the risks of administrator privileges, and the controls for assigning, monitoring, and auditing access.
Prompts and generated responses can contain sensitive information, operational decisions, or business knowledge. This article examines retention and the choice between short-lived records and archiving, based on compliance, resilience, and business-value requirements.
After an application or infrastructure is decommissioned, some data may still be needed to answer audits and meet legal, regulatory, or contractual obligations. This article outlines what to retain and how to manage it.
Generative AI is prompting organisations to rethink access control. An assistant that can search all resources available to an employee may improve productivity, but it also raises risks of data leaks, compliance issues and new attack vectors.
Not all HR data is suitable for AI-assisted recruitment, talent management or workforce planning. This article covers GDPR requirements, discrimination risks and technical threats, then identifies data to exclude from training or inference datasets and governance measures to consider.
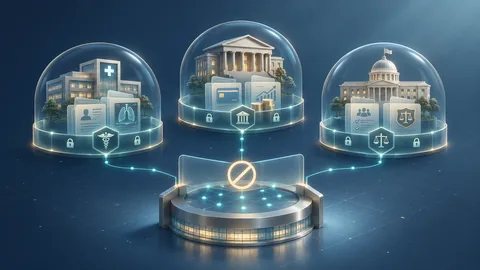
Healthcare, finance and public administration have different requirements for confidentiality, compliance and resilience. Shared infrastructure can create legal, technical and organisational risks. This article compares sector-specific constraints and discusses isolation options and hybrid architectures.
Offboarding must revoke access quickly while preserving a reliable audit trail. This article covers organisational practices, IAM tools and observability solutions for retaining a record of past contributions amid insider threats and compliance requirements.
No articles match. Try a different word or topic.
41 additional articles are available in French. Parcourir les articles français.
Example of history applied to this page.
An initial version of this presentation brings together the software pages and the contract example.
This is the starting point of the history shown here.
Seven situations explain how to find a document, prepare an audit or review a decision.
Each example distinguishes what can be found from the limits that need checking.
The contract has five stages that can be explored by swiping or using the buttons.
A vertical gesture on the document still lets the page scroll normally.
The presentation pages use more familiar words.
The comparison below shows the home-page sentence before and after this change.
Before
KARL Core keeps document versions and recorded decisions. Software for businesses, installed on your servers.
After
KARL Core is software for your business. It keeps document versions and recorded approvals so you can find what changed.
Illustrations explain levels, versions and links between documents.
They support the explanations in this preview.
An initial version of this presentation brings together the software pages and the contract example.
This is the starting point of the history shown here.
Seven situations explain how to find a document, prepare an audit or review a decision.
Each example distinguishes what can be found from the limits that need checking.
The contract has five stages that can be explored by swiping or using the buttons.
A vertical gesture on the document still lets the page scroll normally.
The presentation pages use more familiar words.
The comparison below shows the home-page sentence before and after this change.
Before
KARL Core keeps document versions and recorded decisions. Software for businesses, installed on your servers.
After
KARL Core is software for your business. It keeps document versions and recorded approvals so you can find what changed.
Illustrations explain levels, versions and links between documents.
They support the explanations in this preview.
Example of history applied to this page.